CWP Cage puts every hosting account in its own isolated cage, so a break-in or a runaway script on one site can never reach another account, the panel, or the rest of the server.
ISOLATION
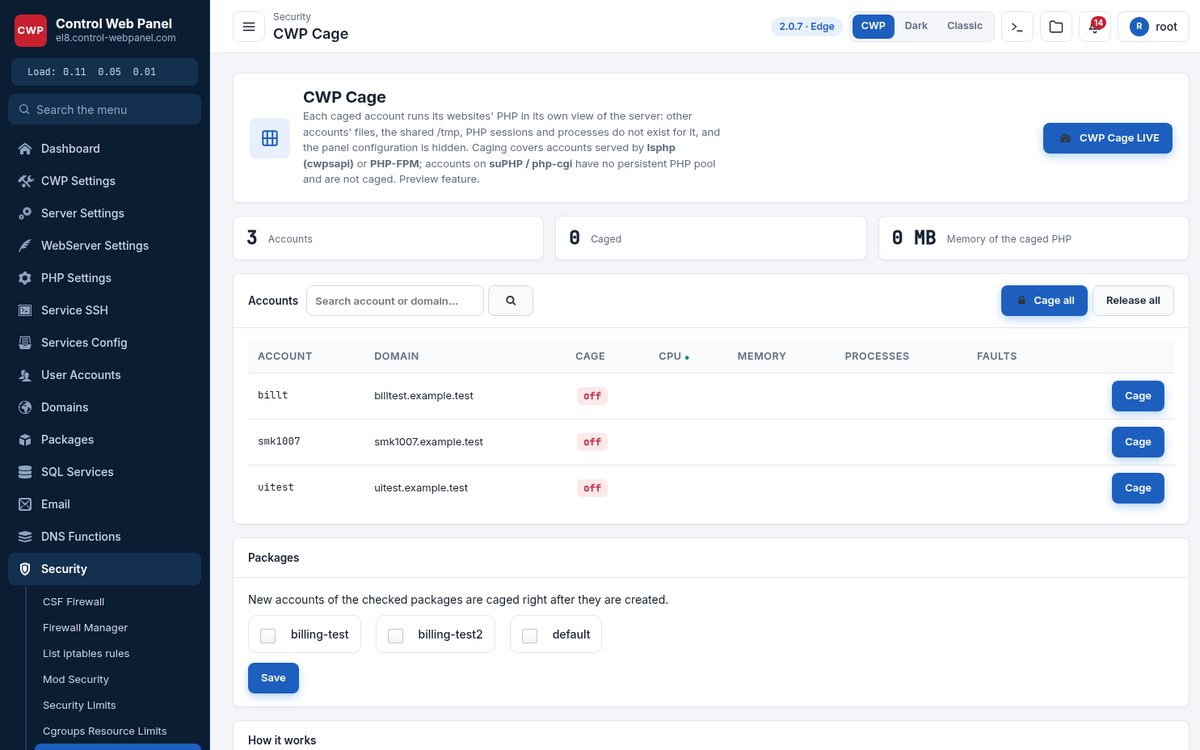
Every account in its own cage
Per-account isolation built from Linux namespaces and cgroups, turned on and off from the panel.
Contained break-ins
A hacked WordPress or a malicious upload stays inside its own cage — it cannot read other accounts’ files, reach the panel ports, or start a crypto miner.
One click per account
Enable or release a cage for any account from the panel. New accounts are caged automatically based on the hosting package they are created from.
Nothing to change in the site
Websites keep working exactly as before — isolation happens at the system level, with nothing to configure inside the application.
LIMITS
Resource limits per package
Give every package fair, enforced limits so one busy account can’t slow down the rest of the server.
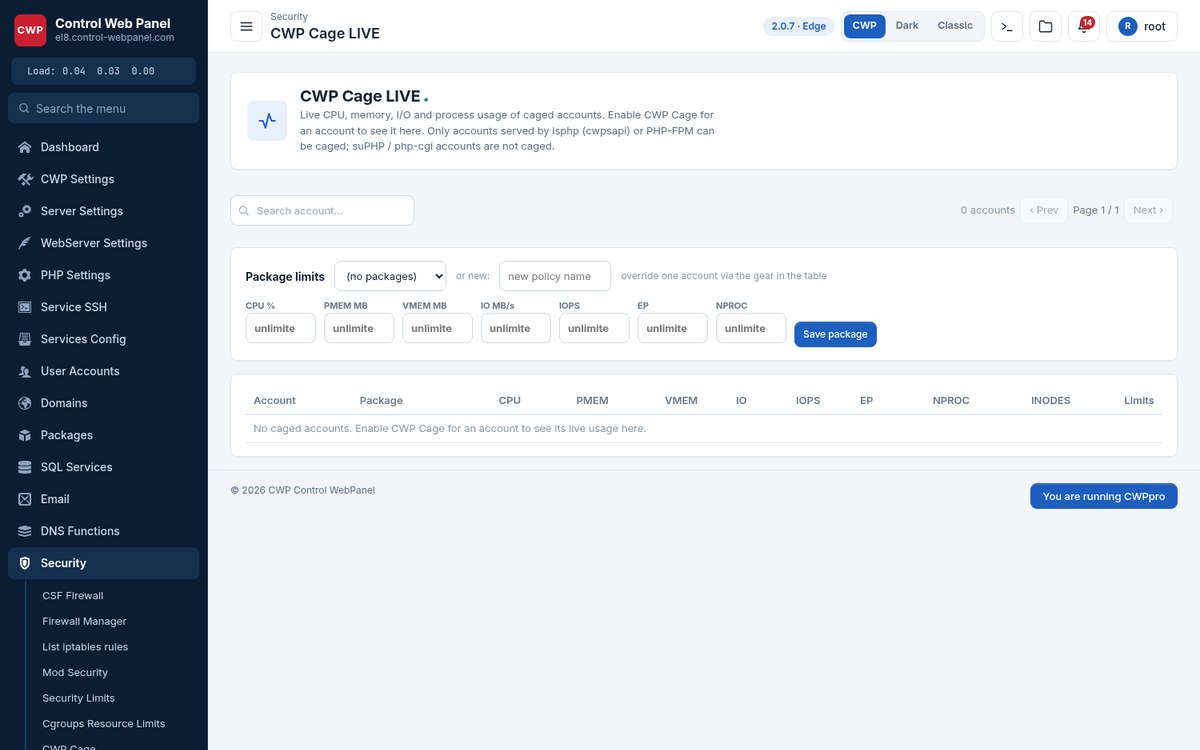
CPU, memory, processes and I/O
Set CPU, memory, process and disk-I/O limits on the hosting package; every account created from it is caged and limited automatically. Watch live usage per cage and adjust the limits as you grow.