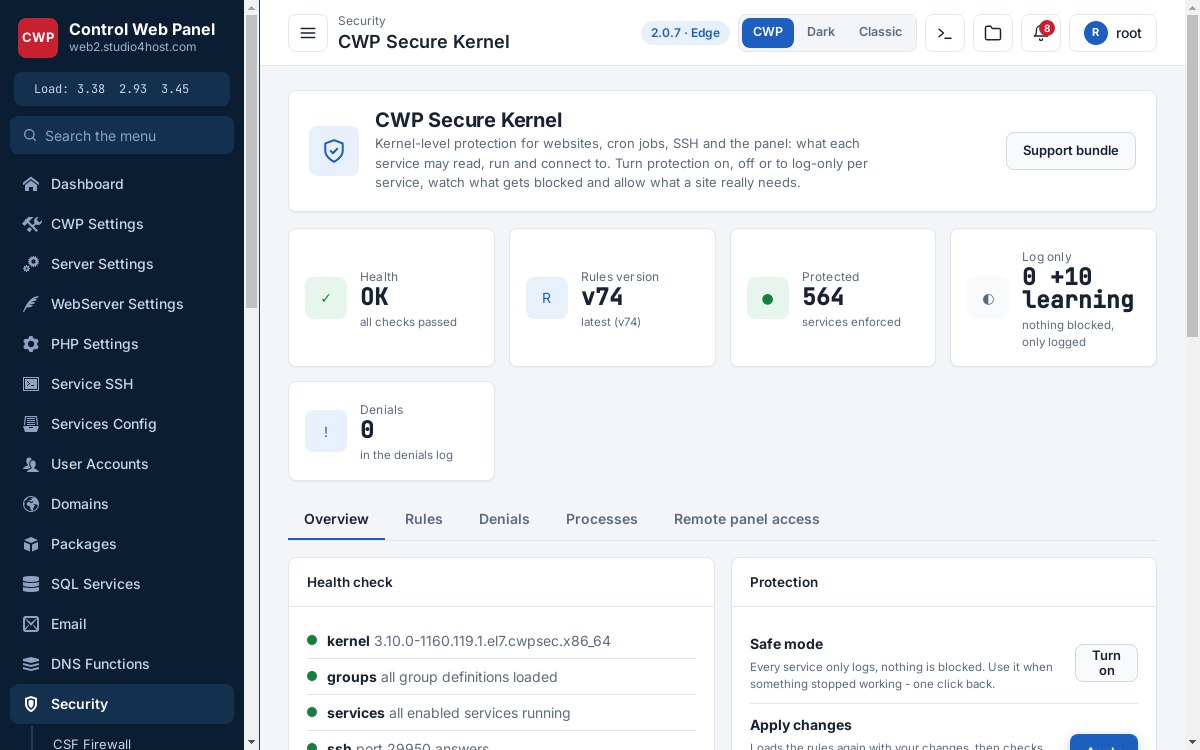
CWP Secure Kernel is protection that starts in the Linux kernel, not in a plugin. Every PHP site, cron job and SSH session runs in its own profile the kernel enforces — a hacked WordPress cannot read other accounts, reach the panel ports or start a crypto miner.
ISOLATION
Every site in its own sandbox
Protection enforced by the kernel — not something a website can switch off.
- A hacked PHP site cannot read other accounts’ files
- Website code is blocked from the panel and system ports
- Crypto miners and unexpected processes are stopped
- Health, rule version and protected services on one page
Contained break-ins
A hacked PHP site, cron job or SSH session stays inside its own kernel profile — it cannot reach other accounts, open the panel or system ports, or run a crypto miner.
One page, full health
Kernel health, the rule version and every protected service are on one page. Safe mode turns everything to log-only with one click if something ever needs it.
Included with support
CWP Secure Kernel comes with every CWP support plan, and new rules are shipped and updated with CWP — nothing extra to maintain.
CONTROL & VISIBILITY
Tune it per service, and see what it blocked
Set the mode for every service, then read blocked actions straight from the kernel.
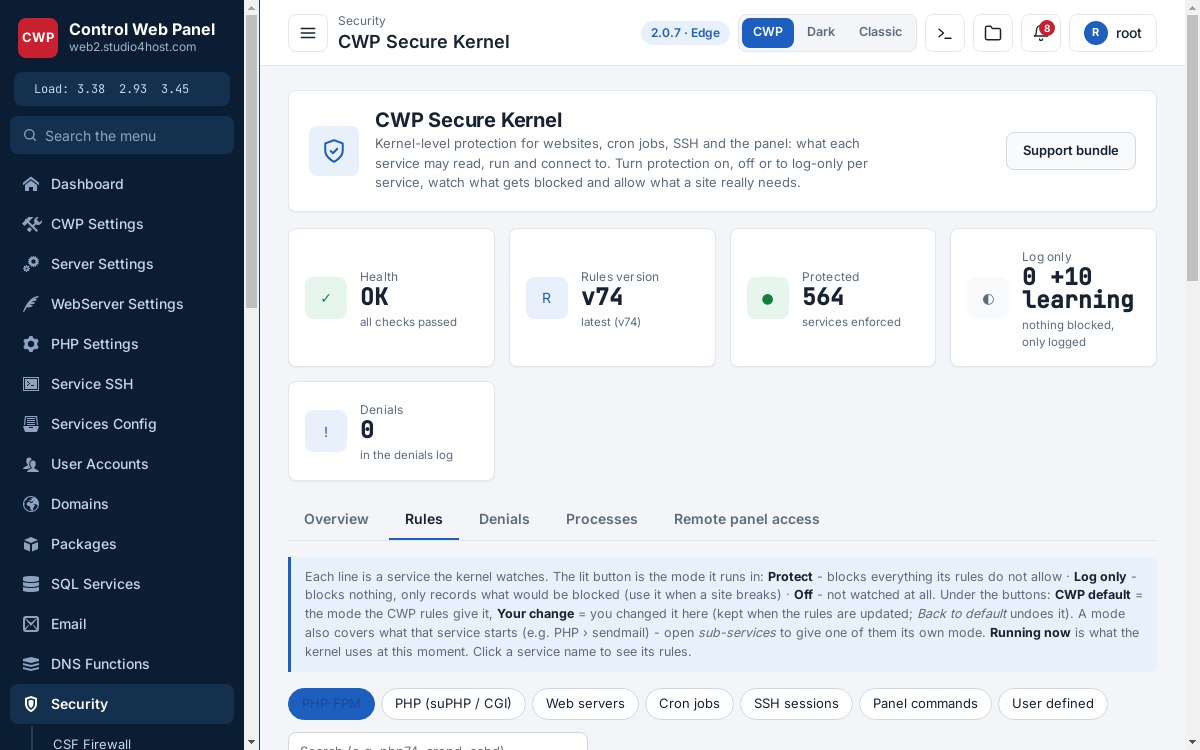
A mode for every service
PHP-FPM, suPHP, the web servers, cron, SSH and the panel commands each run in Protect, Log only or Off. Change one site without touching the rest — your changes are kept when CWP ships new rules.
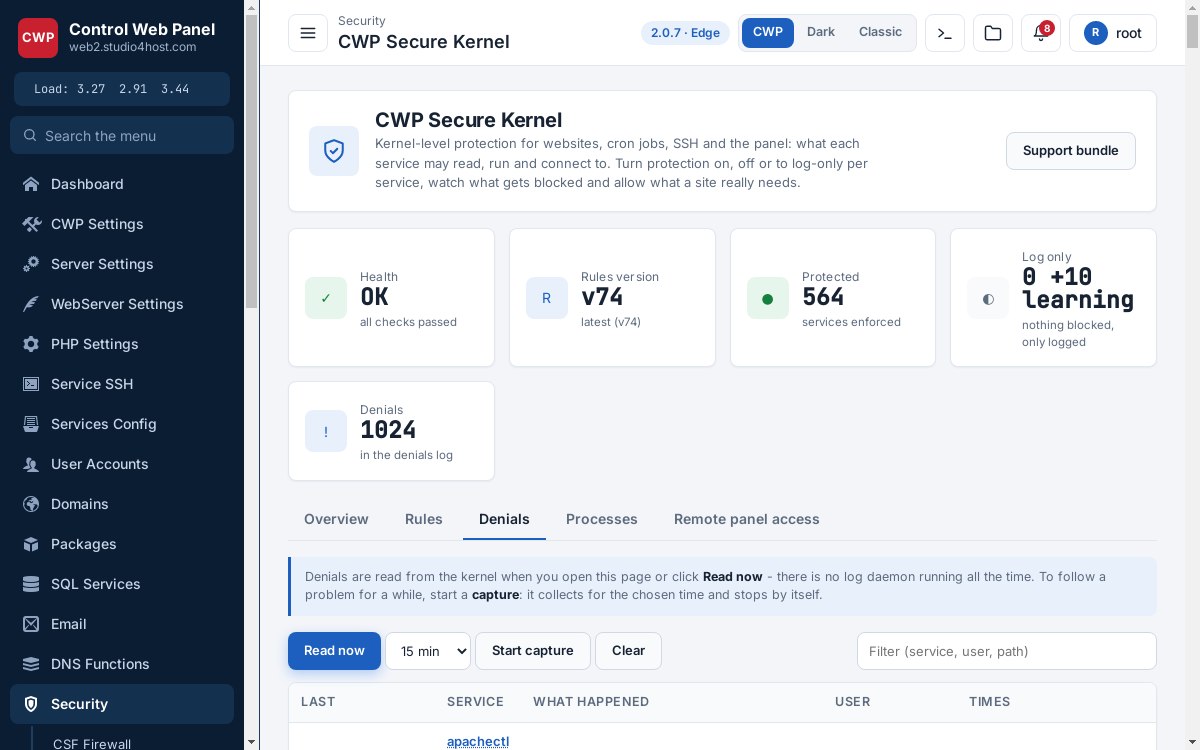
See exactly what was blocked
Blocked actions are read straight from the kernel — no log daemon running all the time. Start a capture to follow a problem and allow exactly what a site really needs.